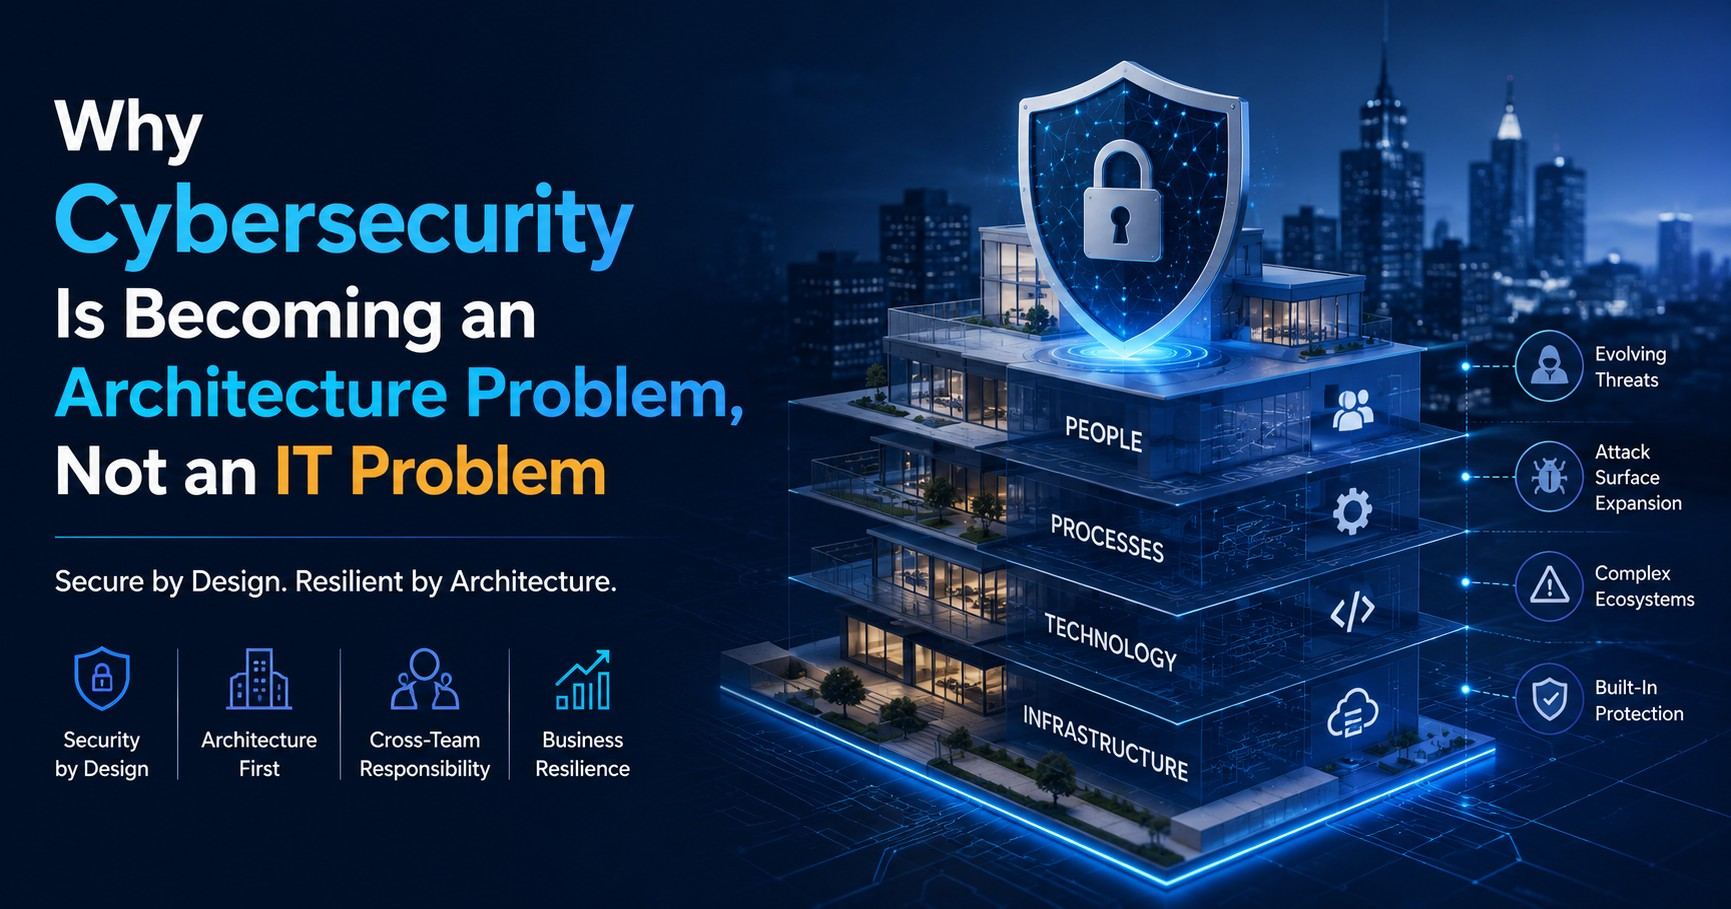
7 Ways a Network Security Management System Strengthens Cybersecurity
-
- September 15th, 2026
- 21 views
Imagine starting your workday and finding that employees cannot access business applications. Emails are delayed, files are unavailable, and customers are reporting strange messages sent from your company accounts.
Your IT team checks the servers, routers, and endpoints but cannot immediately identify where the problem started.
This is where a network security management system becomes important.
Modern businesses depend on connected devices, cloud applications, remote employees, third-party platforms, and digital customer services. As the number of connections grows, keeping track of every potential security weakness becomes increasingly difficult.
A structured network security approach helps businesses monitor their environment, identify suspicious activity, control access, and respond to threats before they become costly incidents.
But what does it actually do, and how can it strengthen cybersecurity?
Let's look at seven practical ways.
Why Network Security Matters More Than Ever
Cyberattacks are no longer limited to large technology companies. Small businesses, startups, financial organizations, healthcare providers, retailers, and professional service firms can all become targets.
According to IBM's Cost of a Data Breach Report 2025, the global average cost of a data breach reached approximately $4.44 million. The report also highlights the growing role of artificial intelligence in both security operations and attacks.
At the same time, businesses are dealing with increasingly distributed environments. Employees may work from home, applications may run across multiple cloud platforms, and sensitive information can move between internal systems and external services.
This creates several security challenges:
Unknown devices connecting to the network
Unauthorized access attempts
Misconfigured firewalls and network devices
Unpatched systems
Phishing and credential theft
Increasing ransomware threats
Limited visibility across cloud and on-premises environments
Weak monitoring of third-party connections
A strong security management strategy helps bring these moving parts under greater control.
7 Ways a Network Security Management System Strengthens Cybersecurity
1. Provides Continuous Network Visibility
One of the biggest security problems is not knowing what is happening inside your network.
A business may have laptops, desktops, servers, smartphones, IoT devices, cloud workloads, wireless access points, and third-party connections operating simultaneously.
Without proper monitoring, suspicious activity can remain unnoticed.
A network security management system provides greater visibility into network activity by helping security teams monitor:
Connected devices
Network traffic
Access attempts
Unusual behavior
Configuration changes
Security events
Potential vulnerabilities
This visibility gives IT teams a clearer picture of their environment.
For example, if an unfamiliar device suddenly connects to an internal network and begins communicating with sensitive systems, monitoring tools can help flag the activity for investigation.
The key benefit: You cannot protect what you cannot see.
2. Detects Suspicious Activity Faster
Cybersecurity incidents can develop quickly.
A stolen password may be used to access an employee account. From there, an attacker could attempt to move across the network, access sensitive files, or install malicious software.
Manual monitoring makes it difficult to identify every suspicious event, particularly for organizations handling thousands of network activities every minute.
Modern security management systems can monitor activity and identify patterns that may indicate a threat.
Examples include:
Repeated failed login attempts
Unexpected traffic spikes
Communication with suspicious destinations
Unusual access outside normal working hours
Abnormal data transfers
Attempts to access restricted systems
Faster detection can reduce the time between an attack beginning and the security team responding.
That matters because every minute of an unresolved incident can increase potential damage.
3. Strengthens Access Control
Not every employee needs access to every business system.
A marketing employee, for example, may need access to customer relationship tools but have no reason to access financial databases.
Weak access controls create unnecessary exposure.
A well-managed network security environment supports principles such as least privilege and role-based access. Users receive access based on what they actually need to perform their responsibilities.
Businesses can also apply controls based on:
User identity
Device
Location
Application
Network segment
Security status
This approach reduces the potential impact of compromised credentials.
If an employee's password is stolen, strong access restrictions can prevent the attacker from automatically reaching every system within the organization.
4. Helps Identify and Address Vulnerabilities
A security system is only as strong as the weaknesses surrounding it.
Outdated software, unsupported devices, incorrect configurations, exposed services, and weak security settings can create opportunities for attackers.
Regular vulnerability identification helps businesses prioritize these weaknesses.
For instance, a security team may discover that:
A network device is running outdated firmware
An unnecessary port is publicly accessible
A firewall rule is too broad
A server has an unresolved security issue
An employee device is missing important updates
Instead of treating every issue equally, teams can prioritize vulnerabilities according to their severity and business impact.
This makes remediation more practical, especially for organizations with limited IT resources.
5. Improves Incident Response
Finding a security incident is only the first step.
The next question is: What should the business do?
Without a defined response process, teams may waste valuable time figuring out who should investigate the incident, which systems should be isolated, and what evidence needs to be preserved.
A managed security environment can support incident response by providing relevant logs, alerts, network activity, and historical information.
This can help security teams answer critical questions:
What happened?
When did it happen?
Which systems were affected?
Which accounts were involved?
Is the threat still active?
What action should be taken?
Businesses using network security management services can also establish monitoring and response processes that match their operational requirements.
The goal isn't simply to detect attacks. It is to contain them before they spread.
6. Supports Compliance and Data Security
Cybersecurity and compliance are closely connected.
Organizations handling personal, financial, healthcare, or confidential business information may need to meet specific regulatory or contractual requirements.
Security frameworks and standards often emphasize areas such as:
Access control
Monitoring
Logging
Risk management
Incident response
Data security
System protection
A structured network security environment can help organizations maintain evidence of security activities and demonstrate that appropriate controls are operating.
For businesses working toward standards such as ISO 27001, effective network controls can become an important part of the broader information security program.
However, compliance should not be treated as a checklist.
The real objective is to reduce security risk while creating a stronger operating environment.
7. Creates a More Proactive Security Strategy
Traditional security often focuses on responding after something goes wrong.
Modern cybersecurity requires a more proactive mindset.
Instead of asking:
"How do we respond to the next attack?"
organizations should also ask:
"What can we identify and fix before an attacker finds it?"
This shift involves combining monitoring, vulnerability management, access controls, security policies, employee awareness, and incident response.
For example, a business might notice repeated suspicious login attempts against a particular application. Rather than waiting for a successful compromise, the security team can investigate the activity, strengthen authentication controls, review exposed systems, and monitor the source more closely.
That is the difference between simply reacting to threats and actively managing security risk.
Key Challenges Businesses Should Address
Implementing security technology alone does not solve every problem.
Businesses should also consider several operational challenges.
Growing Attack Surfaces
Cloud services, remote work, mobile devices, APIs, and connected systems continue to expand the number of potential entry points.
Alert Overload
Security tools can generate large numbers of alerts. Without proper prioritization, important warnings can be buried among low-priority events.
Skills Shortages
Many organizations do not have enough cybersecurity professionals to monitor every security event around the clock.
Poor Configuration Management
Even advanced security tools can become ineffective when firewalls, access controls, network devices, or monitoring rules are incorrectly configured.
Shadow IT
Employees may adopt applications or cloud services without informing IT teams, creating additional security and compliance risks.
Addressing these challenges requires a combination of technology, processes, and skilled oversight.
Practical Steps to Strengthen Network Security
Businesses don't need to transform their entire infrastructure overnight.
A practical starting point is to:
Create an inventory of network-connected devices
Review privileged user accounts
Remove unnecessary access
Update outdated systems and firmware
Review firewall rules regularly
Segment sensitive systems where appropriate
Monitor unusual network behavior
Conduct periodic vulnerability assessments
Establish an incident response procedure
Train employees to recognize common threats
Review third-party network connections
Keep security logs for appropriate periods
These steps can create a stronger foundation before more advanced security capabilities are introduced.
Benefits of a Stronger Security Management Approach
When network security is managed as an ongoing process rather than a one-time project, businesses can gain several advantages.
Better Visibility
Security teams have a clearer view of devices, connections, and network activity.
Faster Response
Suspicious activity can be identified and investigated sooner.
Reduced Exposure
Weak configurations and unnecessary access can be addressed before they become major problems.
Improved Business Continuity
Early detection and response can reduce the potential disruption caused by cyber incidents.
Stronger Compliance Position
Security monitoring and documented controls can support broader governance and compliance efforts.
Greater Confidence
Business leaders can make technology decisions with a clearer understanding of their security environment.
Common Mistakes to Avoid
Even organizations investing in cybersecurity can make avoidable mistakes.
Treating Network Security as a One-Time Project
Threats change continuously. Security controls need regular review and improvement.
Focusing Only on External Threats
Attackers can enter through compromised accounts, infected devices, insiders, or third-party systems. Internal activity matters too.
Ignoring Basic Security Controls
Sophisticated tools cannot compensate for weak passwords, excessive privileges, outdated software, or poor configurations.
Collecting Logs Without Reviewing Them
Having security logs is useful only when someone or something is monitoring and analyzing relevant events.
Choosing Tools Without a Clear Objective
Businesses should first identify their risks and operational requirements. Technology should support the security strategy rather than become the strategy.
Future Trends in Network Security
Network security is changing as business infrastructure becomes more distributed.
AI-Assisted Threat Detection
Artificial intelligence is increasingly being used to analyze large volumes of security data, identify unusual patterns, and help security teams prioritize alerts.
However, AI also creates new risks. Attackers can use AI to automate phishing, generate malicious content, and improve social engineering campaigns.
Zero Trust Security
Zero Trust is becoming increasingly important as businesses move away from assuming that users or devices inside a network are automatically trustworthy.
The approach emphasizes continuous verification, least-privilege access, and stronger identity controls.
Cloud and Hybrid Network Monitoring
As organizations operate across cloud and traditional infrastructure, security teams need visibility across both environments rather than treating them as separate worlds.
Automated Security Response
Automation can help organizations respond to repetitive security events quickly, allowing security professionals to spend more time on complex investigations.
Security Consolidation
Businesses are also looking for ways to reduce fragmented security tools and create more centralized visibility. This can simplify monitoring and help teams respond to incidents more efficiently.
How Data Protection Fits Into Network Security
Network security is closely connected to data protection.
Businesses should consider where sensitive information is stored, who can access it, how it moves across networks, and what happens if an account or device is compromised.
Useful data protection techniques can include encryption, access controls, secure backups, network segmentation, and continuous monitoring.
Similarly, effective data protection methods should cover the entire information lifecycle rather than focusing only on storage.
Organizations should also establish clear data privacy best practices, including limiting unnecessary access, protecting personal information, reviewing third-party access, and securely disposing of information that is no longer required.
A Stronger Network Starts With Better Visibility
Cybersecurity isn't about installing one security product and assuming the problem is solved.
It is an ongoing process of identifying risks, monitoring activity, controlling access, fixing weaknesses, and improving response capabilities.
A network security management system can provide the structure needed to bring these activities together. From stronger visibility and faster threat detection to better access control and compliance support, it can help businesses build a security environment that is prepared for today's connected workplace.
Organizations such as Redkite Network can also help businesses align network security with broader cybersecurity, compliance, and risk-management objectives.
The most important step is to start with visibility. Know what is connected, understand what needs protection, identify where weaknesses exist, and create a clear plan for addressing them.
Because when a threat appears, the businesses that respond fastest are often the ones that prepared before the incident happened.
Frequently Asked Questions
What is a network security management system?
A network security management system is a structured approach for monitoring, protecting, and managing an organization's network. It helps identify threats, control access, monitor activity, and respond to security incidents.
Why are network security management services important?
Network security management services help businesses continuously monitor their network, identify potential weaknesses, manage security controls, and respond to suspicious activity without relying entirely on manual processes.
What are effective data protection techniques?
Encryption, access controls, network segmentation, secure backups, monitoring, and regular security assessments are some commonly used data protection techniques.
How do data protection methods reduce cybersecurity risks?
Data protection methods reduce risk by limiting unauthorized access, protecting information during storage and transmission, and reducing the potential impact of compromised accounts or systems.
What are important data privacy best practices for businesses?
Businesses should limit access to personal information, protect sensitive data, review third-party access, maintain appropriate security controls, and securely remove information when it is no longer needed.